
We analyzed this claim: is it true that
token issuers, lending-protocol guardians and blockchain governors can restrict stolen assets after an emergency without obtaining the wallet holder's consent?
token companies blacklisted stolen coins, a lending system stopped new loans, and a network council moved assets directly, proving that outside administrators hold emergency control across various crypto networks
 ClaraAuthorComing December 1
 RafaVisual artistComing December 1
 JolinaMarketingComing December 1
Who Holds the Power to Freeze Your Crypto
A record heist reveals that code administrators and network councils can immobilize digital assets without a owner's consent.
The story continues
Crypto Networks Seize Control of Stolen Loot
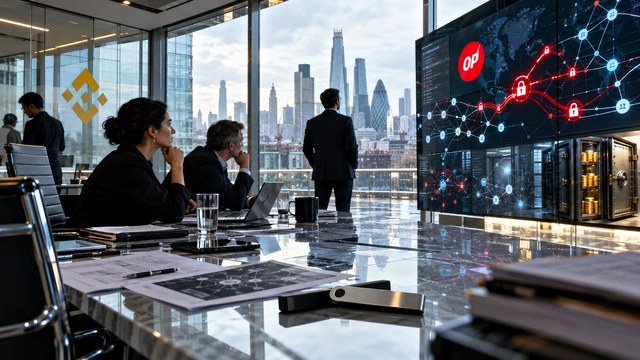
7 November 2026Blockchains are stepping in to freeze loot from the massive Binance theft, overturning a core promise of digital ownership.
In a nutshell
When hackers stole $6.3 billion from Binance on October 29, 2026, the aftermath revealed that digital assets are not immune to outside control. Private companies like Tether and Circle blacklisted stolen tokens, automated lending system Aave froze borrowing, and the Arbitrum network used emergency code updates to take back assets directly. While about $3 billion was successfully immobilized, billions more in native cryptocurrencies like bitcoin and ether cannot be frozen, and none of the halted funds have yet been returned to the exchange.
Highlights
- Attackers drained roughly $6.3 billion from Binance in the largest cryptocurrency theft on record.
- Emergency interventions immobilized approximately $3 billion in stolen digital assets across multiple networks.
- Arbitrum's Security Council temporarily altered its software code to transfer 8,425 ETH and 74.56 million ARB without the holder's approval.
- About $3.23 billion in stolen assets remained beyond ordinary corporate freeze powers.
From the Editor’s Diary
True control over cryptocurrency depends on the specific code behind each asset. While independent coins like bitcoin answer only to their holder's private key, corporate tokens and smart-contract networks remain subject to the administrative powers of those who built them.
Who's involved
Binance
The world's largest digital currency exchange, which holds customer funds in connected accounts
goal → Stop losses, recover stolen funds, and cover customer balances without passing on the costs
Unidentified attackers
The unknown group that took control of Binance withdrawal accounts and moved billions
goal → Convert restricted tokens into untraceable coins and keep the stolen funds
Tether
The private issuer of USDT, a cryptocurrency pegged to the value of the US dollar
goal → Blacklist stolen USDT tokens before thieves can sell them
Arbitrum Security Council
A 12-member emergency governing committee overseeing the Arbitrum blockchain network
goal → Safeguard stolen assets on its network while justifying the use of emergency powers
Circle
The company behind USDC, another major dollar-pegged digital currency
goal → Block stolen USDC balances under its security and compliance rules
Aave guardians and LlamaRisk
Risk advisers and administrators managing the automated Aave lending system
goal → Halt further borrowing against stolen tokens while keeping existing loan markets stable
Ripple
The financial technology company behind RLUSD, a regulated dollar stablecoin
goal → Freeze stolen RLUSD tokens using built-in administrative controls
World Liberty Financial and BitGo
Digital finance ventures associated with the WLFI token and the USD1 stablecoin
goal → Freeze affected balances to stop the stolen tokens from circulating
In short
Ownership in cryptocurrency is not absolute: outside companies and network managers can intervene to stop or seize assets when an emergency strikes. The record $6.3 billion theft from exchange operator Binance showed that digital assets depend heavily on the software rules written into each token.
These interventions make government regulation and formal asset recovery rules likely to expand across blockchain networks.
Whether victims actually recover their funds remains uncertain, because freezing digital money does not automatically send it back.
How it unfolded
A quiet setup precedes an unprecedented digital heist
The attack began quietly when an electronic account was funded through Tornado Cash, an online tool designed to hide the origin of digital money. The operators tested software that would later link to Binance. A public alarm did not sound until an independent analyst posted on social media that an unconfirmed breach was underway.
Automated authorization code allows billions to vanish
The thieves drained wallets across multiple networks using valid digital signatures, possibly obtained through a compromised company laptop. By using a feature that lets basic accounts delegate powers to automated programs, a single instruction stripped billions of dollars from Binance in minutes, triggering worldwide withdrawal suspensions. Once the tokens moved into attacker hands, Binance could no longer control them.
Private token issuers trigger built-in emergency switches
The thieves quickly ran into the legal controls built into dollar-backed tokens, called stablecoins. Issuers like Tether and Circle do not manage the underlying blockchain, but they hold built-in administrative master keys to freeze individual accounts. Both companies blacklisted the attacker accounts, immobilizing over a billion dollars in stolen tokens, though hundreds of millions escaped before the switches flipped.
Automated lending protocols halt new transactions
Before defenses went up, an attacker deposited stolen stablecoins into Aave, a decentralized digital lending pool, and borrowed millions in ether. Aave's risk stewards responded by halting new deposits and borrowing across hundreds of markets. But because the system lacked the power to cancel contracts retroactively, it could not seize the borrowed ether. Other token issuers quickly froze representations of gold and staked tokens, demonstrating that administrative control attaches to token contracts rather than raw digital assets.
A blockchain governing council steps in to redirect funds
A governing committee on the Arbitrum network took a far more aggressive step. Instead of merely freezing balances, its 12-member Security Council temporarily updated its underlying system code to create a bypass function. This enabled the council to move stolen ether and ARB tokens directly into an administrative safe house without the thief's signature. The action stopped those assets from escaping, but it also proved that network managers can override the basic rule that only account holders control their money.
Frozen money remains stranded rather than restored
Halting tokens prevented further sales, but it did not return the money to Binance. While returning the billions will require complex legal and technical steps, Binance pledged to cover the entire loss from its reserves. Around half of the stolen funds remained in tokens like native ether and bitcoin, which have no corporate issuer and cannot be frozen from afar.
Where things stand
Issuers have demonstrated that they can lock stolen token balances, lending guardians can halt credit, and blockchain councils can rewrite network code to move funds. These emergency powers differ in scope: a blacklist leaves funds trapped in place, lending freezes stop future transactions while leaving old loans intact, and chain-level overrides shift ownership entirely. None of these actions automatically return the assets to Binance.
The investigation remains open. Official agencies have not confirmed whether North Korean state hackers carried out the raid, and no formal vote has released the funds held in Arbitrum's vault. More than $3 billion remains beyond the reach of corporate freeze controls, leaving the ultimate recovery of the stolen wealth unresolved.